AI
AI Threat Detection: Real Benefits and Hidden Costs
Machine learning detects novel patterns but creates blind spots when attackers mimic normal traffic, requiring human validation.
Machine learning detects novel patterns but creates blind spots when attackers mimic normal traffic, requiring human validation.
NoSQL injection bypasses traditional input validation because the database engine interprets logical operators within the query structure itself.
Most policy failures stem from ignoring the hidden data exfiltration paths created by automated agent workflows and shadow integration endpoints.
Most breaches fail not because of weak code, but because stolen credentials allow attackers to bypass security entirely.
Small teams face unique risks from AI jailbreaks because generic security tools often miss subtle social engineering embedded in code or data requests.
Data subject rights transform legal obligations into engineering constraints that require deterministic data lineage and automated access controls across distributed systems.
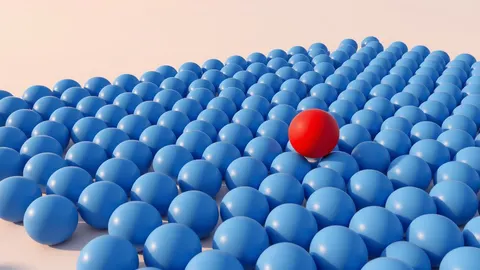
Fraud detection models do not identify bad actors directly. They measure how far a transaction deviates from the statistical norm of accepted behavior.
Embedding security into the development lifecycle prevents costly late-stage fixes, but it adds friction to every commit and requires a cultural shift that resists automation.
Fine-tuning adjusts model weights for specific tasks but rarely improves general reasoning, creating a hidden cost in maintenance and evaluation overhead that many teams overlook.
Remote desktop abuse rarely begins with a brute-force login; it usually starts with a stolen credential moving silently through lateral pathways before the session opens.
Single-source denial of service tests reveal infrastructure resilience, while distributed tests expose your ability to filter malicious traffic from legitimate users.
Monitoring detects statistical drift, not logical errors, meaning a model can be statistically stable while producing harmful or incorrect outputs that bypass standard checks.
Most organizations fail at intrusion detection because they prioritize volume over context, creating alerts that hide real threats rather than revealing them.
Executive impersonation attacks succeed not through technical flaws, but by exploiting the psychological pressure of urgency and hierarchy within your organization.
Unapproved tools often bypass network security, creating hidden channels where sensitive data leaks without triggering any monitoring alerts.
Attackers replicate domain controller databases locally to extract hashes without triggering standard authentication logs or alerting on network traffic.
USB drop attacks hide in plain sight, using hardware enumeration events and delayed execution to bypass standard network perimeter defenses.
Models memorize specific data points rather than general patterns, allowing attackers to reconstruct private information from standard model outputs without accessing source code.
Clipboard hijackers operate silently in memory without files, making traditional signature-based detection ineffective against their rapid data exchange.
Mandatory periodic resets increase credential theft risk by encouraging predictable password patterns and reducing user memory capacity.
Most API security failures stem from logic errors in business workflows, not from missing authentication headers or basic network misconfigurations.
You must treat AI agents as privileged code execution contexts, not just text generators, to prevent silent data exfiltration and unauthorized system changes.
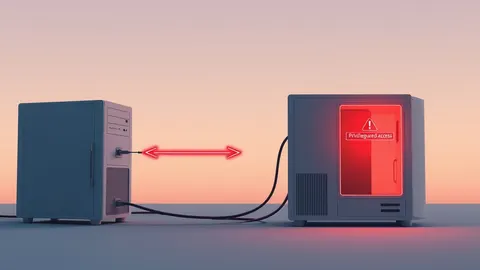
NTLM relay attacks exploit legacy authentication protocols to escalate privileges without ever stealing the actual password hash from the network traffic.
Define agent security boundaries, map control points to data flows, and identify where standard application defenses fail to protect autonomous reasoning.