Threat Intelligence
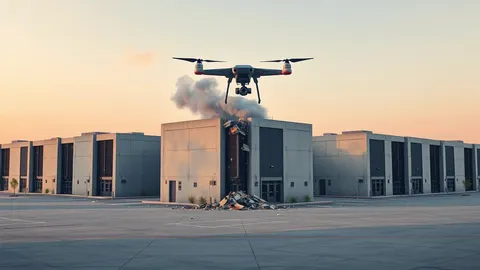
Physical drone strikes on Yandex data centers disrupt Russian cloud and AI services
Ukrainian drone attacks on three Yandex facilities force emergency mode and raise concerns about data loss and AI training delays.
Threat Intelligence coverage from Sandbox Desk holds 19 articles, 18 of them reference guides. The newest was published on October 16, 2026. New stories are added as soon as they are confirmed, from more than 150 sources checked as often as every 45 seconds. Each story lists its sources. Primary sources we follow for this section include FIRST: Forum of Incident Response and Security Teams and MITRE ATT&CK.
Ukrainian drone attacks on three Yandex facilities force emergency mode and raise concerns about data loss and AI training delays.
Attackers use native system utilities to bypass security controls and maintain access, making routine task audits a primary defense strategy.
Ticket-granting tickets remain valid until expiration, allowing attackers to move laterally without passwords or local admin rights on the compromised host.
Golden ticket attacks bypass standard password checks by forging Kerberos tickets with infinite lifetimes, rendering most endpoint defenses useless.
Service accounts with weak encryption settings allow attackers to request and crack tickets offline without triggering immediate detection alerts.
Attackers hide command channels inside standard domain name queries, bypassing firewalls that trust recursive resolvers and ignore payload inspection.
Hacktivists exploit structural gaps in identity and data flow rather than complex software bugs to achieve maximum visibility with minimal technical effort.
A national cyber emergency declaration shifts incident response from voluntary coordination to mandatory federal support, altering data retention and reporting obligations immediately.
The Diamond Model converts raw network noise into structured adversary profiles, allowing small teams to prioritize threats based on capability rather than volume.
Most threat reports provide context rather than detection rules, forcing security teams to translate vague narratives into specific defensive actions.
Open source intelligence relies on correlating fragmented public data rather than accessing hidden systems, making data hygiene more critical than tool selection for accurate results.
Effective defense relies on reducing noise through precise telemetry and validating controls with structured adversary emulation rather than chasing every alert.
Intelligence provides the context for known threats while hunting relies on assumption-driven searches to find hidden activity that data alone cannot reveal.
Runbooks turn panic into procedure by removing decision fatigue during outages, allowing teams to act faster than their training alone permits.
Adversary emulation reveals that your controls work on paper but fail in practice by simulating specific threat behaviors rather than running generic vulnerability scans.
Most incident response runbooks fail because they assume human cognition remains stable under stress, leading responders to skip critical validation steps when pressure mounts.
Remote desktop abuse rarely begins with a brute-force login; it usually starts with a stolen credential moving silently through lateral pathways before the session opens.
Attackers replicate domain controller databases locally to extract hashes without triggering standard authentication logs or alerting on network traffic.
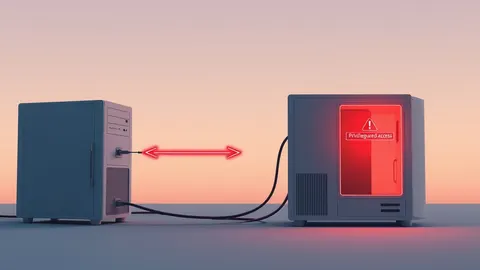
NTLM relay attacks exploit legacy authentication protocols to escalate privileges without ever stealing the actual password hash from the network traffic.