Vulnerabilities
Null Pointer Dereference: Immediate Response and System Recovery
A null pointer dereference often indicates deeper memory corruption that can allow remote attackers to execute arbitrary code on your servers.
Everything Sandbox Desk has reported about incident response: 13 stories, newest first. Part of our Threat Intelligence coverage.
A null pointer dereference often indicates deeper memory corruption that can allow remote attackers to execute arbitrary code on your servers.
Tabletop exercises expose decision-making gaps in security processes by simulating attack scenarios without requiring technical execution or live system changes.
Keeping logs longer does not improve security; it increases the attack surface for data exfiltration and raises the cost of every audit.
Command and control channels hide inside normal traffic patterns, making protocol inspection alone insufficient for detection without behavioral context.
Recovery time depends on how often you verify backup integrity, not on how much data you store or how fast your servers run.
Treating ransomware as a simple encryption event ignores the lateral movement and data exfiltration that determine whether you can recover without paying.
Hacktivists exploit structural gaps in identity and data flow rather than complex software bugs to achieve maximum visibility with minimal technical effort.
A national cyber emergency declaration shifts incident response from voluntary coordination to mandatory federal support, altering data retention and reporting obligations immediately.
Most breaches begin as accidental leakage, not malicious exfiltration, because human error bypasses controls that only flag intentional theft.
Effective defense relies on reducing noise through precise telemetry and validating controls with structured adversary emulation rather than chasing every alert.
An AI agent with tool access can execute code changes silently, meaning containment requires revoking execution permissions rather than just blocking network traffic.
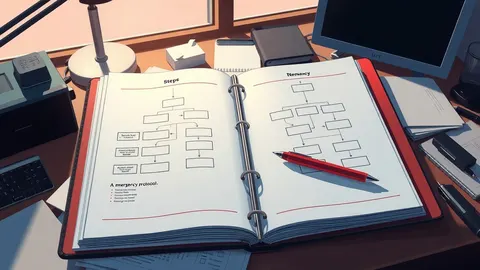
Runbooks turn panic into procedure by removing decision fatigue during outages, allowing teams to act faster than their training alone permits.
Most incident response runbooks fail because they assume human cognition remains stable under stress, leading responders to skip critical validation steps when pressure mounts.