AI
McDonald's Faces Legal Challenge as MPC-HC Gets Visual Update and New Surface Devices Announced
The latest tech news cycle features a legal challenge against McDonald’s, a visual update for MPC-HC, and new Surface hardware announcements.
The latest tech news cycle features a legal challenge against McDonald’s, a visual update for MPC-HC, and new Surface hardware announcements.
Satya Nadella urges organizations to assume advanced AI models are compromised and step back to assess their underlying trust structures.
Security initiatives are using lifelike AI chatbots to trick cybercriminals into wasting time on fake victims, reducing their operational efficiency.
Automated systems can alter operator displays and control physical machinery, creating a blind spot for current industrial security defenses.
Detection tools measure statistical patterns, not truth, causing consistent false positives that disrupt legitimate workflows and erode trust in automated systems.
Ukrainian drones struck a Yandex facility housing supercomputers used for AI model training, disrupting operations for Russia's leading search engine provider.
Investors face challenges comparing AI leaders because Anthropic reports gross sales via cloud partners while OpenAI records only its net share.
A Chinese actor utilized ARTEX AI and Claude agents to infiltrate financial systems, exposing organizational vulnerabilities in automated security defenses.
The law ties legal liability to the technical architecture of your system, meaning you can face penalties for data errors in models you did not train yourself.
An AI agent with tool access can execute code changes silently, meaning containment requires revoking execution permissions rather than just blocking network traffic.
The OWASP LLM Top 10 is a diagnostic lens for architectural flaws, not a checklist of vulnerabilities to patch before you ship your model to production.
AI usage policies shift risk management from perimeter defense to behavioral oversight, addressing threats that traditional security tools cannot see.
Jailbreaking relies on prompt engineering, not code exploits, and often fails because modern models filter output as well as input.
Formal risk frameworks reduce catastrophic failure rates but often increase deployment latency and obscure novel attack vectors that evade standard detection.
Most models hide their reasoning, but you can reconstruct the decision path by isolating input variables and tracking output shifts over time.
Monitoring output accuracy alone misses silent data drift and prompt injection vectors that degrade model utility and security over time.
Large language models shift security from rule-based filtering to probabilistic reasoning, exposing new risks in how teams validate automated decisions and handle sensitive context.
Large language models predict the next word using statistical probability, not by accessing a database of verified facts or understanding meaning.
Generative AI shifts security from reactive auditing to continuous validation, catching logic errors before they reach production.
Machine learning shifts security from static rule matching to dynamic behavior analysis, allowing teams to detect novel threats that bypass traditional signature-based defenses.
Machine learning detects novel patterns but creates blind spots when attackers mimic normal traffic, requiring human validation.
Most policy failures stem from ignoring the hidden data exfiltration paths created by automated agent workflows and shadow integration endpoints.
Small teams face unique risks from AI jailbreaks because generic security tools often miss subtle social engineering embedded in code or data requests.
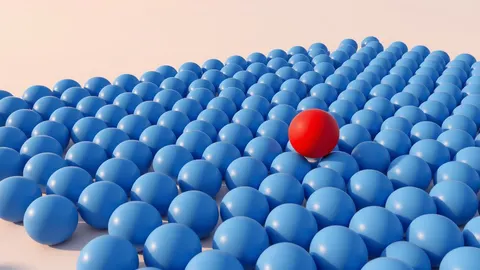
Fraud detection models do not identify bad actors directly. They measure how far a transaction deviates from the statistical norm of accepted behavior.